• Welcome to ASR. There are many reviews of audio hardware and expert members to help answer your questions. Click here to have your audio equipment measured for free!

AliExpress webpage keeping multipoint Bluetooth headphones active with WebAudio fingerprinting

829

Active Member
Joined
Jul 27, 2021
Messages
154
Likes
191
Hi all,

I recently stumbled over this: AliExpress webpage keeping multipoint Bluetooth headphones active with WebAudio fingerprinting

Found a classification by security researcher Mike Kuketz (machine translated):
"[...] The problem is not so much audio fingerprinting alone. What is crucial is the combination of many small characteristics that can be used to create a fairly precise profile of the browser and device. Hardly anything can be seen by users. And >reject cookies< isn't enough. What helps? uBlock Origin. The discoverer provides two specific filter rules that block the AliExpress scripts in question. In his test, the site continued to work afterwards."

I find this quite alarming and it makes me wonder whether maybe we have become a little blinded by the dazzling measurement results from some manufacturers - and careless as a result. Granted, I am thinking a step beyond AliExpress but there have been potentially unpleasant discoveries like here; and also manipulated USB devices could pose a threat. Nobody ever tested for IT-security issues on audio gear, as far as I know. I mean, it's nothing that has not happened in one way or the other before; like with:


What do you think and how do you make sure your affection towards audio is not being exploited by third parties to their own benefit?

Let us discuss. :)
 
Nowadays, I believe that all is already invented. Only smal and still small modification(s) of previously invented things.

I am reader of some of the classic books relative to electronics: Gray, Langford Smith, Seeley, Seely, Millman, and others; and reading them you will found that olny changed the form of the same theory is implemented with new elements. By the the way, the standard 555 chip oscillator is not too diferent from the Phantastron and Sanatron circuits from the war years. So, I don't alarm about circuit copies and evolution.
 
If you use the internet at all, you are being exploited in many ways.

It may be a fair exchange - your data for free services, say - but I'd prefer to be told the truth upfront in simple form, and make an informed decision on things like fingerprinting or "excess telemetry".

So for example, AliX should have a simple statement on the landing page that briefly explains what they get and why. Any site not doing this should be blocked, IMHO. Companies hide behind pages of impenetrable legalise, and that's often a sign they are shafting you right off the bat, IMHO.

I tend to have an unsubstantiated view that I'm at more risk with Chinese products that can link to the internet. It's one of the reasons I bought a UK-brand for my streamer (but who knows what still gets reported home?) and that I play music form my own collection of CD-ripped files rather than stream. As they say, just because I'm paranoid doesn't mean they are not all out to get me! I'm not, and neither am into conspiracy theories - it usually comes down to global capitalism having rights that transcend those of individuals or even states, in a democracy.

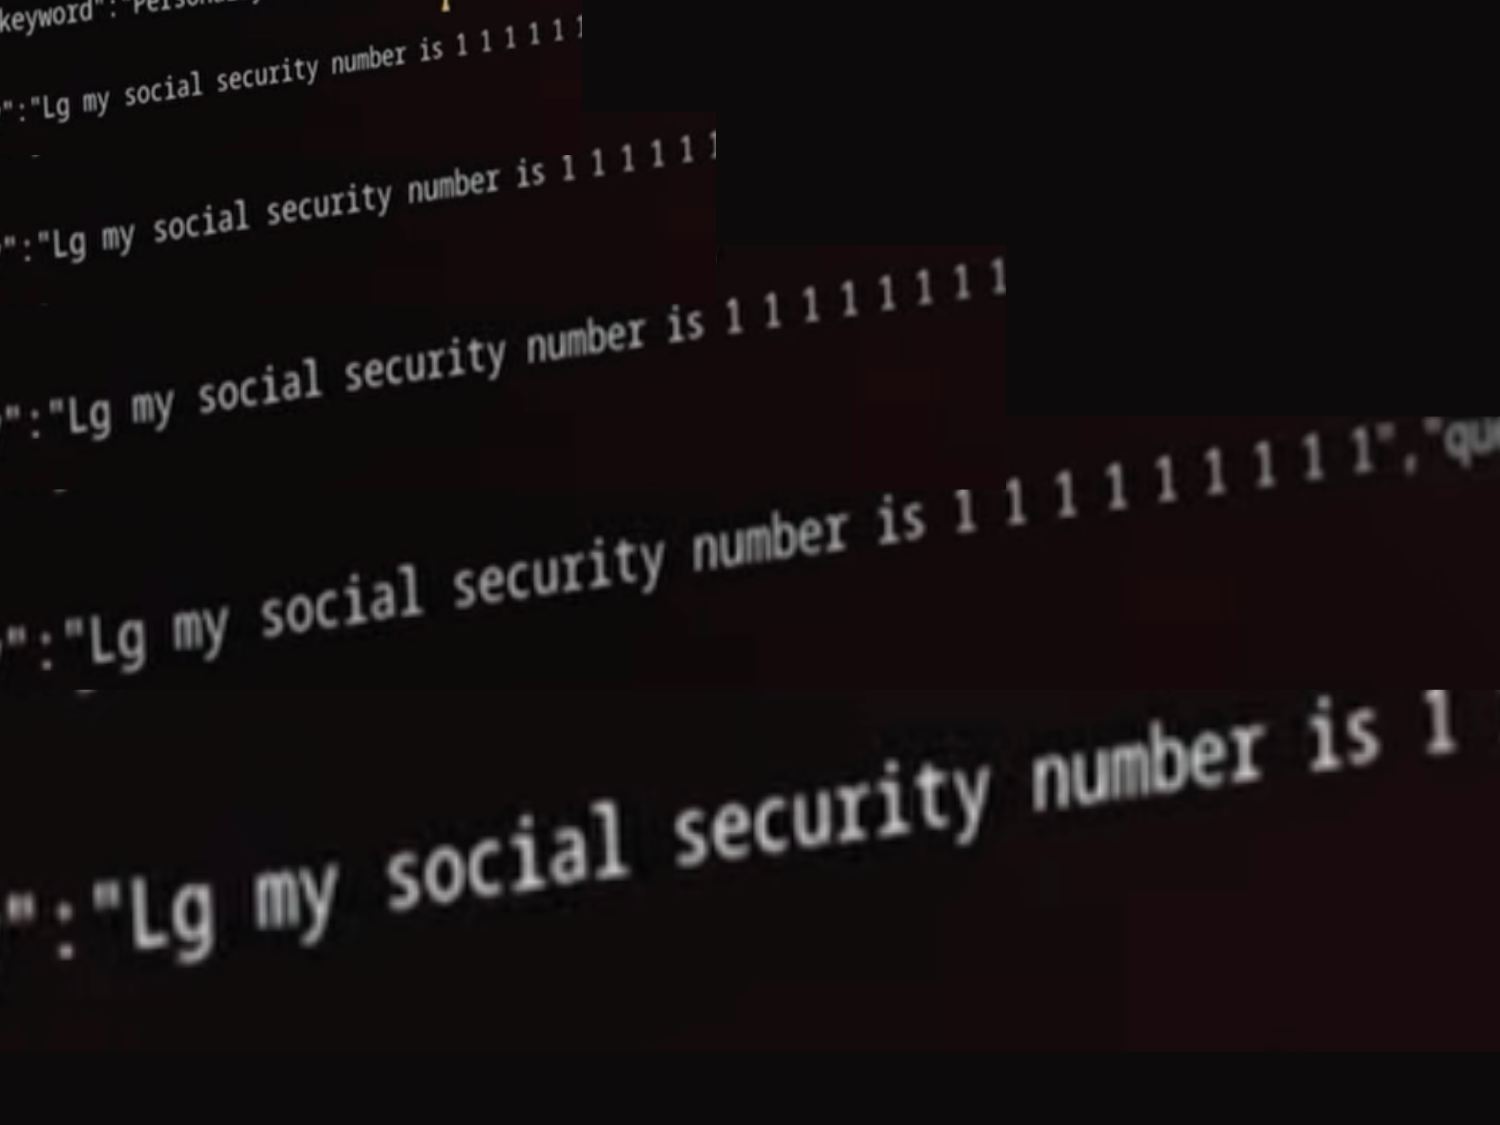
On a related note about LG TV privacy invasion (topical of late), I was trying to think of a quick way in my router to block the TV's outbound internet access (except to user "white listed sites", for example, iPlayer, ITVx ) while letting it get from from my LAN. I thought it would be dead easy, but it's not with my router - I think I'll need an RPi or similar on the LAN to be the local DNS look-up point, so I can log and remove certain access. There may be other ways. This is not going to affect browser-borne fingerprinting of course, but may automated telemetry. I will look into RPi DNS control, as I'm sure there are products that do this and maybe more - any pointers welcome. I wish I had not sold my RPi, albeit for a tiny profit!
 
What do you think and how do you make sure your affection towards audio is not being exploited by third parties to their own benefit?
This is an unusual bug to have audio devices actually active due to browser fingerprinting but the tech and practices involved are very common. If you aren't blocking every type of tracking with a plugin, your browsing habits are being collected for commercial purposes. Audio and Ali Express really aren't the headlines here.

The really concerning thing is that this type of data (and much, much, much more) is for sale to pretty much anyone, including the government and surveillance firms like Palantir.
 
I find this quite alarming
Have you seen the LG smart TVs spying issue?
LG of course denies
 
Back
Top Bottom